HR10671Referred to Committee
Securing Our Critical Infrastructure Act
Introduced
In Committee
3
Passed One Chamber4
Passed Both5
Signed into Law119th
Congress
2026-10-01
Introduced
4
Cosponsors
HR
ⓘType
Sponsor
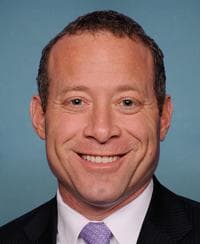
Josh Gottheimer
Democrat · NJ · Representative
Votes with party: 90.7% (589 recorded votes)
Full profile: /officials/G000583
Source: Congress.gov · FEC
Cosponsors (4)
Members who have signed on to support this bill since introduction. Source: Congress.gov.
Latest Action
The most recent step in the bill's legislative path. Committee Activity below shows referrals and reports; the full action-by-action history including floor proceedings lives at Congress.gov →
Committee Activity
Currently in
- House Committee on Homeland SecurityReferred To · 2026-10-01
Plain-English Summary
Plain-English summary pending. Introduced on 2026-10-01. Check back soon — summaries are generated as bills progress through Congress.
Full Bill Text
Verbatim text published on Congress.gov via GovInfo. Use Cmd+F / Ctrl+F to search within this excerpt.
[Congressional Bills 119th Congress] [From the U.S. Government Publishing Office] [H.R. 10671 Introduced in House (IH)] <DOC> 119th CONGRESS 2d Session H. R. 10671 To amend the Cyber Incident Reporting for Critical Infrastructure Act of 2022 to reauthorize a program of the Cybersecurity and Infrastructure Security Agency relating to security vulnerability warnings, and for other purposes. _______________________________________________________________________ IN THE HOUSE OF REPRESENTATIVES October 1, 2026 Mr. Gottheimer (for himself, Mr. Bacon, Mr. Nunn of Iowa, Ms. Scholten, and Mr. Landsman) introduced the following bill; which was referred to the Committee on Homeland Security _______________________________________________________________________ A BILL To amend the Cyber Incident Reporting for Critical Infrastructure Act of 2022 to reauthorize a program of the Cybersecurity and Infrastructure Security Agency relating to security vulnerability warnings, and for other purposes. Be it enacted by the Senate and House of Representatives of the United States of America in Congress assembled, SECTION 1. SHORT TITLE. This Act may be cited as the ``Securing Our Critical Infrastructure Act''. SEC. 2. REAUTHORIZATION OF A PROGRAM OF THE CYBERSECURITY AND INFRASTRUCTURE SECURITY AGENCY RELATING TO SECURITY VULNERABILITY WARNINGS. Section 105 of the Cyber Incident Reporting for Critical Infrastructure Act of 2022 (6 U.S.C. 652 note) is amended-- (1) in the heading-- (A) by striking ``ransomware'' and inserting ``security''; and (B) by striking ``pilot''; (2) in subsection (a)-- (A) by striking ``Not later than 1 year after the date of enactment of this Act, the Director shall establish a ransomware vulnerability warning pilot program'' and inserting ``There is established in the Cybersecurity and Infrastructure Security Agency a security vulnerability warning program''; and (B) by striking ``associated with common ransomware attacks''; (3) by striking ``pilot'' each place it appears; (4) in subsection (b)(1), by striking ``utilized in ransomware attacks and mitigation techniques'' and inserting ``for information systems, and mitigation techniques relating thereto''; (5) in subsection (d), by striking ``covered entities'' and inserting ``covered utilities''; (6) in subsection (e)-- (A) by striking ``No procedure'' and inserting the following: ``(1) In general.--No procedure''; and (B) by adding at the end the following new paragraphs: ``(2) Exemption from disclosure.--Information shared by a covered entity with respect to the program established under subsection (a) is exempt from disclosure under section 552(b)(3) of title 5, United States Code, and any provision of State, local, or Tribal freedom of information law, open government law, open meetings law, open records law, sunshine law, or similar law requiring disclosure of information or records. ``(3) Prohibited activity.--The Director may not disclose, retain, or use information shared by a covered entity with respect to the program established under subsection (a) unless such disclosure, retention, or use, as the case may be, is for a purpose specified in subsection (d)(5)(A) of section 105 of the Cybersecurity Information Sharing Act of 2015 (6 U.S.C. 1504). ``(4) Privacy.--The Director shall retain information shared by a covered entity with respect to the program established under subsection (a) in a manner that protects from unauthorized use or disclosure any of the following: ``(A) Any personal information that is of a specific individual and included in such retained information. ``(B) Any information that identifies a specific individual and is included in such retained information.''; and (7) by striking subsection (g) and inserting the following new subsections: ``(g) Cyber Hygiene Services.-- ``(1) Automatic enrollment.--As part of the program established under subsection (a), the Director shall automatically enroll in the applicable cyber hygiene services of the Cybersecurity and Infrastructure Security Agency each covered utility. ``(2) Disenrollment.--A covered utility enrolled in a cyber hygiene service pursuant to paragraph (1) may disenroll from such service by submitting to the…
Show the remaining 214 wordsHide the remaining 214 words
Director notice of such disenrollment. ``(h) Incident Response.--As part of the program established under subsection (a), if the Director determines that a covered utility has been affected by a cyber incident, the Director shall utilize the incident response capabilities of the Cybersecurity and Infrastructure Security Agency to carry out on behalf of such utility a response to such incident, as appropriate. ``(i) Coordination.--In carrying out the program established under subsection (a), the Director shall coordinate with the Administrator of the Environmental Protection Agency. ``(j) Termination.--The program established under subsection (a) shall terminate on the date that is five years after the date of the enactment of this subsection. ``(k) Covered Utility Defined.--In this section, the term `covered utility' means an entity that is any of the following: ``(1) A water or wastewater utility that serves not more than 100,000 individuals. ``(2) An eligible entity (as such term is defined in section 40124 of the Infrastructure Investment and Jobs Act (42 U.S.C. 18723)). ``(3) An operator of any of the following: ``(A) A public water system (as such term is defined in section 1401 of the Safe Drinking Water Act (42 U.S.C. 300f)). ``(B) Treatment works (as such term is defined in section 212 of the Federal Water Pollution Control Act (33 U.S.C. 1292)).''. <all>
Related legislation
Bills by the same sponsor or covering overlapping subjects.
- HR10757To provide for a limitation on contributions to the United Nations.Referred to Committee · 2026-10-06
- HRES1618Recognizing the third anniversary of the October 7, 2023, terrorist attacks on Israel, honoring the victims and the hostages, and calling for the complete disarmament of Hamas for a durable end to the war in Gaza.Referred to Committee · 2026-10-06
- HRES1612Honoring Captain Smit Machchhar and the crew and passengers of Flydubai Flight 1073, and condemning the attempted terrorist attack on that flight.Referred to Committee · 2026-10-05
- HR10670China FIREWALL Act of 2026Referred to Committee · 2026-10-01